Quantum-resistant encryption is the use of cryptographic algorithms designed to stay secure against attacks from both classical and quantum computers. For a bank, adopting those algorithms is the visible part of the work. The harder part is knowing where today’s public-key cryptography runs, what it protects, who depends on it, and in what order it can safely change.
That is the real evaluation question. Choosing an algorithm is a standards decision. Choosing an approach to readiness is an operating decision, and it determines how much of the migration a bank can actually see, test and control.
Quantum Infinite built Quantum Authority™ for that second decision: a platform for cryptographic intelligence and post-quantum readiness inside the bank’s own environment. First, though, the questions any bank should ask of any approach.
What Is Quantum-Resistant Encryption?
Quantum-resistant encryption is commonly used to describe encryption methods designed to resist attacks from future, sufficiently capable quantum computers. The broader term post-quantum cryptography (PQC) also includes digital-signature algorithms, not just encryption or key establishment. PQC algorithms run on conventional computers; their security is based on mathematical problems not known to be efficiently solvable by quantum computers.
It differs from quantum key distribution (QKD), which uses quantum physics and specialized hardware to distribute keys. QKD and PQC solve different problems, and most banks planning migrations are working with PQC because it runs on existing infrastructure.
The migration focus is primarily public-key cryptography, including RSA and elliptic-curve systems used for key establishment and digital signatures. Symmetric cryptography, such as AES, is affected differently and generally requires a different risk response; banks should follow current standards and their cryptographic risk assessment rather than assume every algorithm needs the same treatment. The technical case behind this is covered in how Shor’s Algorithm threatens RSA, so the focus here stays on the bank’s decisions.
One note on language. No cryptographic system carries an absolute guarantee, which is why “quantum-resistant” is the more accurate phrase than any claim of being unbreakable.
Why Banks Need a Structured Approach to Quantum-Resistant Encryption
A bank’s public-key cryptography is spread across far more than one platform. It sits in customer authentication, payment services, digital certificates, APIs, internal applications, legacy systems, secure messaging and a long list of third-party integrations.
Three conditions make a structured approach necessary.
Long confidentiality lifetimes. Account records, identity documents and legal files may need to stay private for many years. Data copied today can still matter later, a point explained in Harvest Now, Decrypt Later (HNDL).
Dependency complexity. Replacing an algorithm in one application can affect certificates, key management, partner connections and vendor software that the bank does not own.
Operational continuity. Payment and authentication systems cannot be taken offline to test a cryptographic change. Interoperability and rollback have to be planned before anything moves.
None of this calls for urgency theater. It calls for an approach that produces evidence, order and control. For the wider banking context, see post-quantum cryptography for financial institutions.
What Banks Should Evaluate Before PQC Migration
Cryptographic Discovery and Inventory
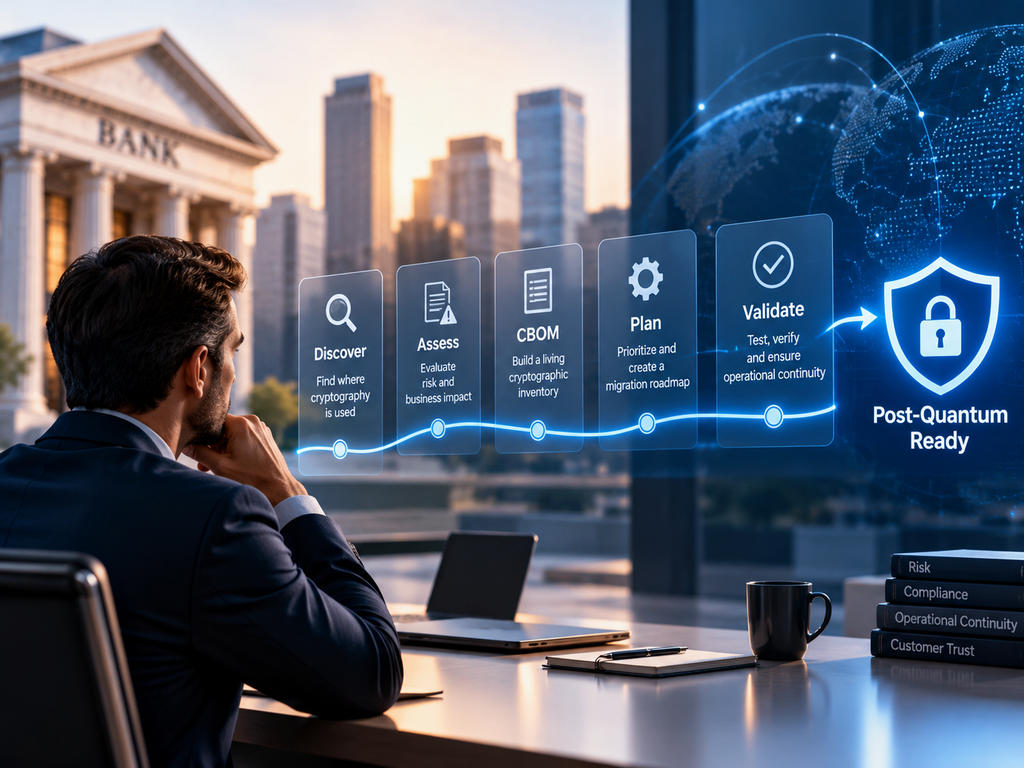
Discovery should surface cryptography across applications, infrastructure, certificates, protocols and third-party interfaces, including systems nobody has touched in years. Incomplete visibility is the main planning risk: a migration plan is only as accurate as the list of assets behind it. A bank should ask how discovery works, what it can and cannot see, and how gaps are recorded rather than hidden. The methodology is outlined in why cryptographic discovery comes first.
Cryptographic Risk Assessment and Business Impact
Not every finding deserves equal attention. A useful assessment weighs algorithm strength, system criticality, data sensitivity, confidentiality lifetime, the quality of the evidence behind each finding and dependency complexity. Evidence quality matters more than it sounds. A finding confirmed by direct inspection and one inferred from a configuration note should not carry the same weight in a prioritization decision.
Cryptographic Bill of Materials (CBOM)
A Cryptographic Bill of Materials is a structured record of the cryptographic components in a system and where they are used. Think of it as a software bill of materials for cryptography. A living CBOM connects each asset to its cryptographic components, the evidence collected, findings, risk and remediation status, so it stays useful after the first assessment instead of becoming a static report.
Migration Planning, Interoperability and Validation
Planning should reflect system readiness, dependencies, vendor support and business priorities. Before production changes, a bank needs validation, interoperability checks, approvals and a rollback plan. Ask who owns each migration step, what conditions must be met before a system moves, and how vendor actions are tracked.
Data Sovereignty and Deployment Control
Cryptographic assessment data is sensitive. It describes where a bank’s protections are strong and where they are not. Banks should ask where that data is processed, who can access it, and whether the deployment model supports auditability and change control. An on-premises, bank-controlled model keeps that information inside the institution’s environment.
What Should Banks Look for in a PQC Readiness Platform?
Use these criteria to compare any approach, including tools built in-house.
| Evaluation criterion | Questions a bank should ask | Why it matters |
| Discovery coverage | Does it cover applications, infrastructure, certificates, protocols and third-party interfaces? How are blind spots reported? | Unseen assets become unplanned migration work. |
| Evidence quality | Is each finding tied to evidence? Can confidence levels be reviewed? | Prioritization is only as reliable as the evidence behind it. |
| Risk prioritization | Does it weigh data sensitivity, confidentiality lifetime and system criticality? | Limited teams need a defensible order of work. |
| Dependency mapping | Can it show internal and vendor dependencies for each asset? | Hidden dependencies cause delays and outages. |
| CBOM | Is the CBOM maintained over time and linked to findings and remediation status? | A static inventory goes out of date quickly. |
| Migration workflows | Are owners, vendor actions, readiness conditions and approvals tracked? | Migration is a coordination problem as much as a technical one. |
| Validation | Does it support interoperability testing, continuity checks and rollback planning? | Payment and authentication systems have little tolerance for failure. |
| Auditability | Are decisions and changes recorded for review? | Examiners and internal audit may ask for the trail. |
| Data control | Where does assessment data live and who controls the environment? | Findings about weak spots are sensitive in themselves. |
How Quantum Authority™ Supports Bank PQC Readiness
Quantum Authority™ is Quantum Infinite’s platform for cryptographic intelligence and post-quantum readiness for banks. Mapped to the criteria above, its documented capabilities are:
- Discovery: cryptographic discovery across applications, infrastructure, certificates, protocols and third-party interfaces.
- Assessment: evaluation of algorithm strength, system criticality, data sensitivity, confidentiality lifetime, evidence quality and dependency complexity.
- CBOM: a living Cryptographic Bill of Materials linking assets, cryptographic components, evidence, findings, risk, dependencies and remediation status.
- Prioritization: ranking based on risk, business impact and migration urgency.
- Migration planning and workflows: planning based on readiness, system dependencies, vendor support and business priorities, with workflows covering owners, dependencies, vendor actions, readiness conditions, remediation and approvals.
- Validation: interoperability considerations, operational continuity and rollback planning.
- Operating model: bank-controlled, on-premises execution that emphasizes data sovereignty, auditability and change control.
- Ongoing visibility: continuing cryptographic visibility to support crypto-agility, meaning the ability to change algorithms, keys and certificates without rebuilding systems.
A platform is one part of the picture. Quantum Infinite specialists and engineers work around it inside the institution’s environment, which is where the judgment calls on sequencing, vendors and risk tolerance get made. Quantum Authority™ supports that work. It does not replace it, and it does not remove the need for a bank’s own governance and decisions.
Learn more about Quantum Authority™, Quantum Infinite’s bank-first cryptographic intelligence and migration platform. For broader implementation support, explore Quantum Infinite’s PQC services for banks.
How NIST PQC Standards Fit Into a Bank’s Migration Planning
In August 2024, NIST finalized three post-quantum cryptography standards: FIPS 203 (ML-KEM), a key-encapsulation mechanism used for key establishment; FIPS 204 (ML-DSA), a digital-signature standard; and FIPS 205 (SLH-DSA), a stateless hash-based digital-signature standard. NIST’s post-quantum cryptography project maintains standardization updates, while its NCCoE migration project addresses practical migration challenges.
The standards define what migrated cryptography looks like. They do not tell a bank where its cryptography is, which systems come first, or how vendors will cope. Selecting an algorithm is the end of the technical decision and the beginning of the migration work.
NIST standards are also not, by themselves, a legal mandate for every private U.S. bank. They are the technical reference that vendors, federal systems and industry guidance are building toward. For the regulatory picture, see Quantum Infinite’s regulations and mandates overview. For migration sequencing, see the PQC migration roadmap for financial institutions.
Frequently Asked Questions
What is quantum-resistant encryption?
Quantum-resistant encryption uses algorithms designed to remain secure against both classical and quantum computers. It is closely tied to post-quantum cryptography and mainly replaces public-key methods such as RSA and elliptic curve cryptography.
How is post-quantum encryption different from traditional encryption?
Traditional public-key encryption relies on factoring or discrete logarithm problems that a large quantum computer could solve. Post-quantum encryption relies on different mathematical problems not known to be efficiently solvable by quantum computers, and it runs on conventional hardware.
Why do banks need to assess cryptographic readiness before migration?
Migration changes certificates, keys, protocols and vendor connections across many systems. Without an assessment, a bank cannot see what exists, what is most exposed or what depends on what, so sequencing becomes guesswork.
What is a Cryptographic Bill of Materials (CBOM)?
A CBOM is a structured record of the cryptographic components used across systems and where they appear. A living CBOM also tracks evidence, findings, risk and remediation status as the environment changes.
How do NIST PQC standards affect bank migration planning?
FIPS 203, 204 and 205 give banks a standardized technical target. They do not replace discovery, risk assessment, vendor coordination or testing, and they are not automatically a legal requirement for every private bank.
What should a bank look for in a PQC readiness platform?
Look for broad discovery coverage, evidence-backed findings, risk prioritization, dependency mapping, a maintained CBOM, migration workflows, validation support, audit trails and control over where assessment data is processed.
What is Quantum Authority™?
Quantum Authority™ is Quantum Infinite’s platform for cryptographic intelligence and post-quantum readiness for banks. It supports discovery, assessment, a living CBOM, prioritization, migration planning and validation within a bank-controlled, on-premises model, alongside Quantum Infinite specialists.
Prepare Your Institution for Post-Quantum Readiness
Quantum-resistant encryption only protects what a bank can find, rank and safely change. Visibility, evidence, risk prioritization and controlled migration are what turn a standards decision into a workable program.
If your institution is evaluating its approach, Quantum Infinite can discuss PQC readiness and how Quantum Authority™ may fit your environment. Explore the Quantum Authority™ platform, review PQC services for banks, or contact Quantum Infinite.
References: NIST PQC (nist.gov/pqc); NIST NCCoE Migration to PQC (nccoe.nist.gov/applied-cryptography/migration-to-pqc); NIST FIPS 203, 204 and 205; Bank for International Settlements quantum-readiness roadmap for the financial system.